
Following the $6.3 Billion: Inside the Binance Exploit with Lukka Blockchain Analytics
On October 29, 2026, an attacker drained roughly $6.3 billion from Binance hot wallets on ten blockchains, most of it in about 20 minutes. It is the largest crypto theft on record, more than four times the $1.5 billion taken from Bybit in February 2025.
Six days later, the visible crisis has eased. Binance says it has covered about 95% of the shortfall with its own funds, withdrawals reopened on November 1, and the FBI has named North Korea’s TraderTraitor unit as responsible. For Binance customers, the story is largely over.
For everyone else, it is just starting. About $3 billion in stablecoins was frozen. More than $3 billion in Bitcoin, Ether, XRP and other assets that no issuer can freeze is still in the attacker’s hands, and it has started to move. Every exchange, OTC desk, bank and payment firm that touches digital assets is now a potential exit point.
We traced the attacker’s wallets in Lukka Blockchain Analytics to show what that looks like below the headlines: where the money went in the first hours, how the laundering network is structured, and what compliance teams should be watching for now.
Where things stand on November 3
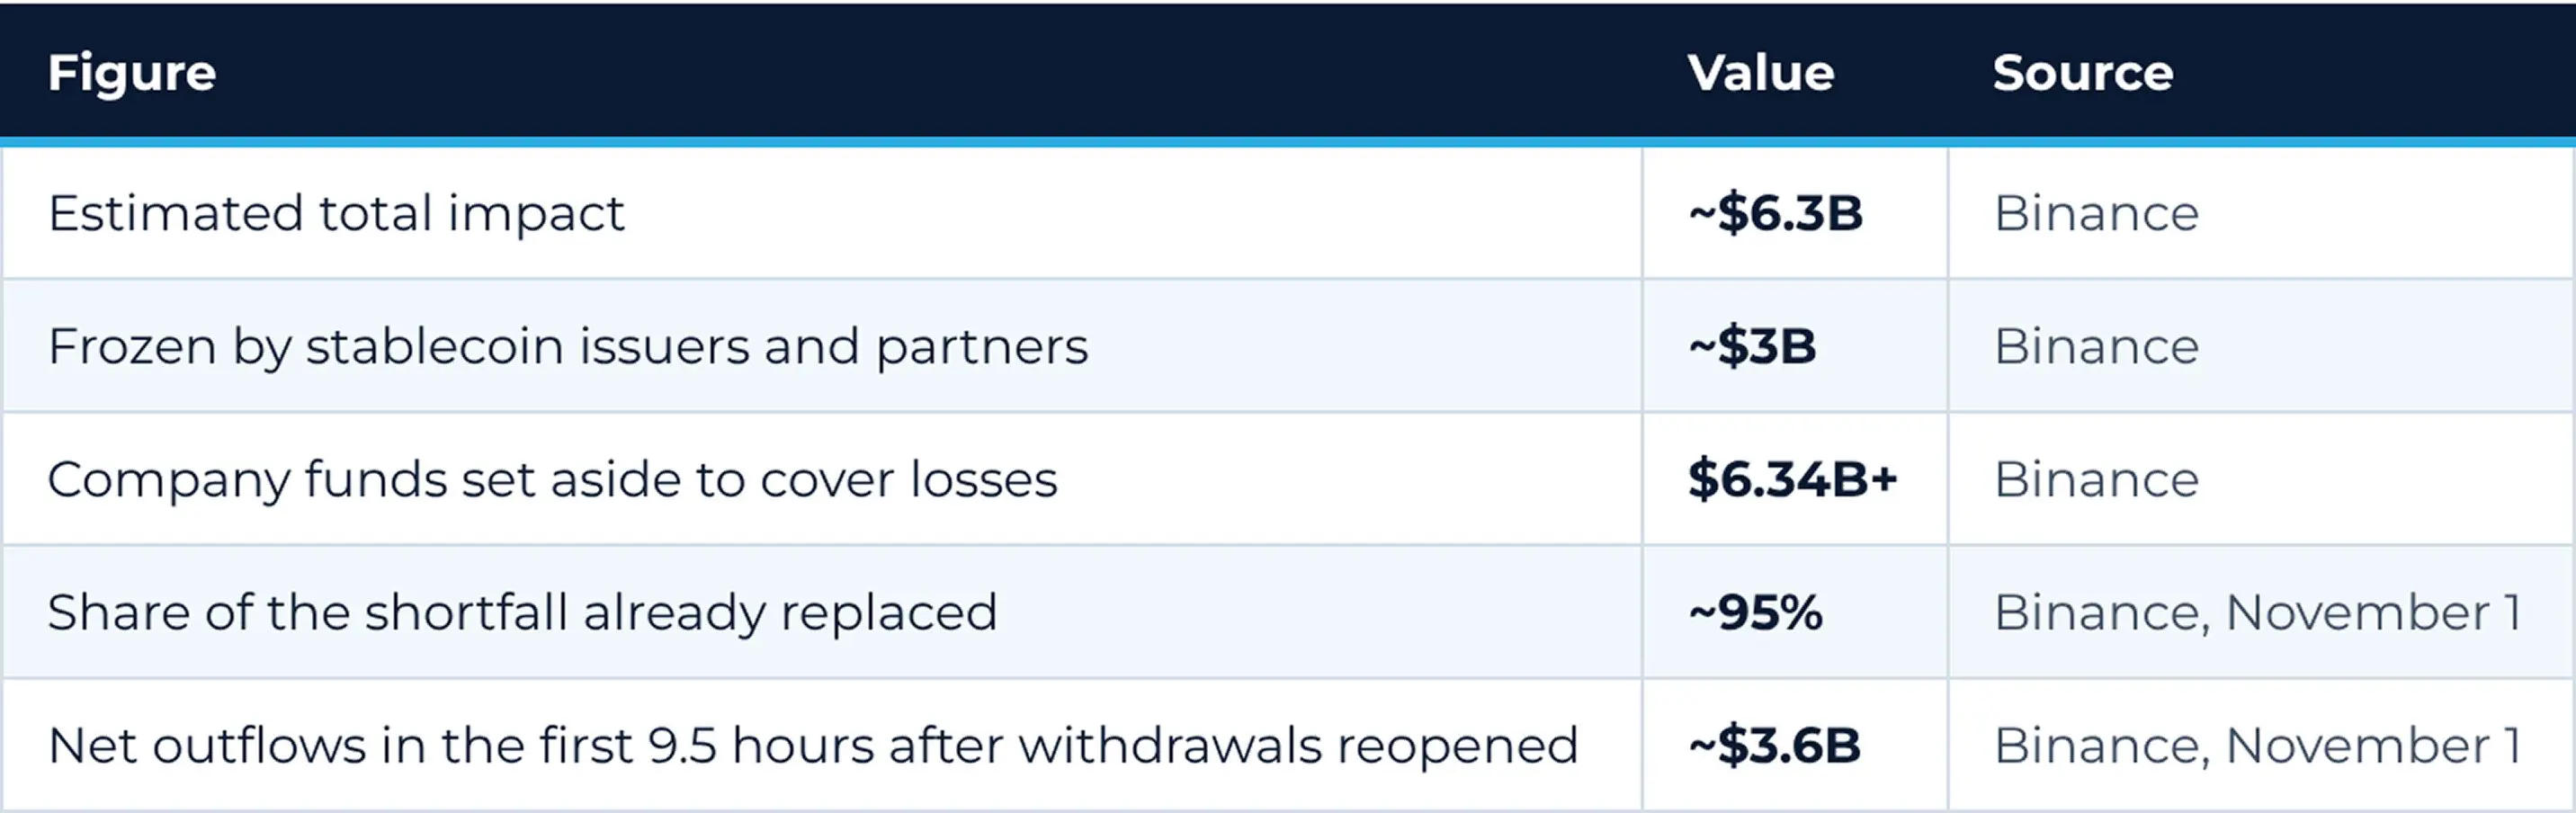
Customers. Binance replaced stolen balances using part of its Secure Asset Fund for Users (SAFU), its Futures Insurance Fund and its corporate treasury, buying tokens through market and OTC channels. The remaining 5% is in less liquid tokens. On November 2, Binance completed a zero-knowledge Proof of Reserves based on an October 31 snapshot, showing 10 assets, including BTC, ETH, USDT and USDC, backed at least 1:1. A second snapshot covering more tokens is scheduled for November 4.
Root cause. Binance’s initial investigation points to a compromised DevOps engineer’s laptop, which gave the attacker access to a service container that could submit withdrawal transactions. Binance has since reported additional points of breach, and co-CEO Richard Teng has said the attacker “did not simply use one engineer’s permissions” and used malware designed to erase evidence. A full post-mortem has not been published.
Attribution. On October 31, the FBI attributed the theft to TraderTraitor, a North Korean state-backed hacking unit, and published wallet addresses linked to the stolen funds. The FBI, U.S. Secret Service and IRS Criminal Investigation are investigating, and asked exchanges, DeFi services and node operators to block transactions tied to those addresses.
Recovery. Frozen is not the same as recovered. No frozen funds have been returned yet; returning them typically requires legal process, potentially across several jurisdictions.
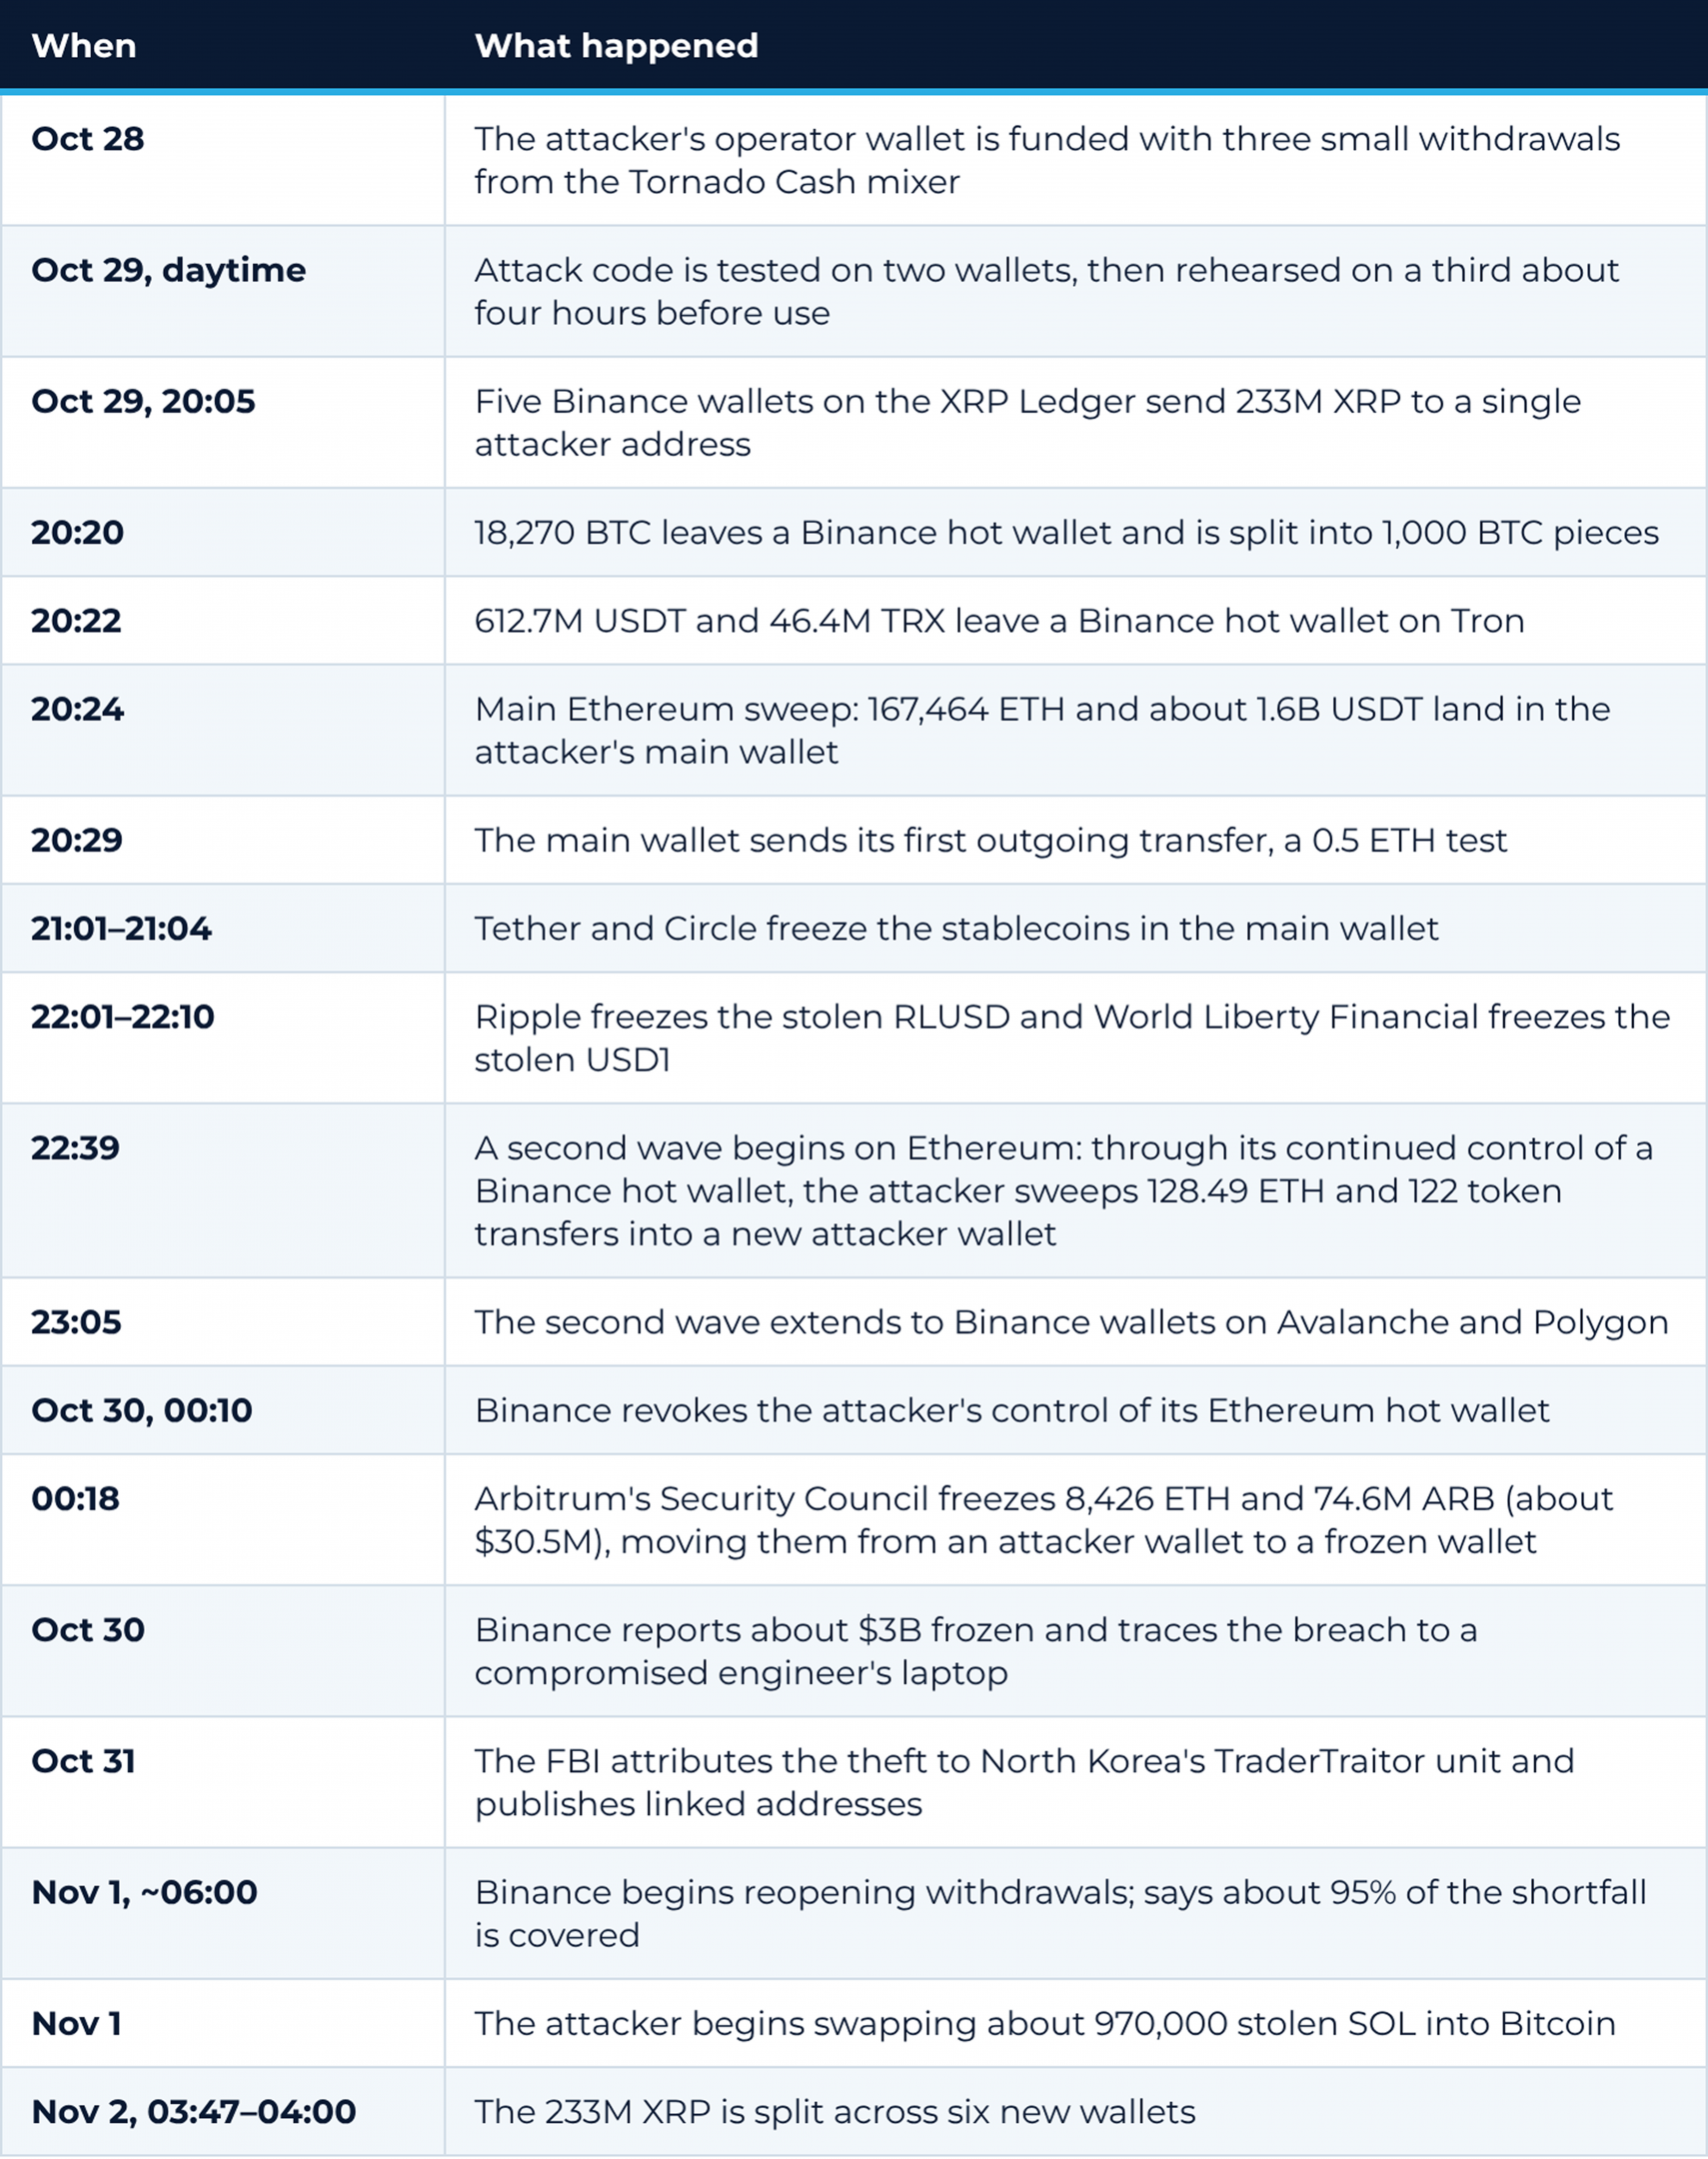
Timeline (UTC)
The keys held. The process didn’t.
Binance says it has found no evidence that private keys were stolen. The on-chain record points somewhere more uncomfortable: the attacker appears to have made Binance’s own signing systems approve transactions of its choosing.
Wallets on chains with different key types and signing schemes all produced valid signatures for the attacker within about half an hour. On Ethereum, the attacker used EIP-7702, a feature added in the 2025 Pectra upgrade that lets a wallet hand its behavior to a smart contract. It submitted 50 pre-signed authorizations, one for each possible transaction count, so that one would be valid when it landed. That handed control of a Binance hot wallet to a contract only the attacker could call, and the attacker used it to sweep new deposits at least six more times over the next three and a half hours.
The pattern matches earlier attacks attributed to the same group, including Bybit: patient staging, a compromised person or device inside the organization, and the cryptography left intact. For any institution running its own digital asset operations, the questions are about governance:
Signing access. Who and what can request a valid signature from your signing infrastructure?
Delegation alerts. Would an unexpected wallet authorization, such as an EIP-7702 delegation on a treasury wallet, trigger an alert?
Segregation. Are approval paths separated by chain and wallet tier, or could one compromise reach them all?
Inside the trace: the attacker’s main wallet
The attacker’s main receiving wallet on Ethereum is 0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c. Lukka Blockchain Analytics labels it as belonging to a hacker in the Binance exploit, notes that Tether has blacklisted it, and scores it 99 out of 100, high risk. Screenshots below were captured on October 30; figures in the text are from a Lukka report run on November 4.
It is part of a much larger network. Lukka’s latest report names the wallet’s owner as Lazarus Group, the umbrella name for North Korea’s state hacking operations, and links it to a cluster of 10,161 addresses controlled by the same owner. It also flags the wallet as related to a subject on sanctions lists and to a comprehensively sanctioned country, marks its geographic risk as sanctioned (North Korea), and lists ransomware among the owner’s profiles. That changes the compliance question from “is this stolen?” to “is this sanctions exposure?”
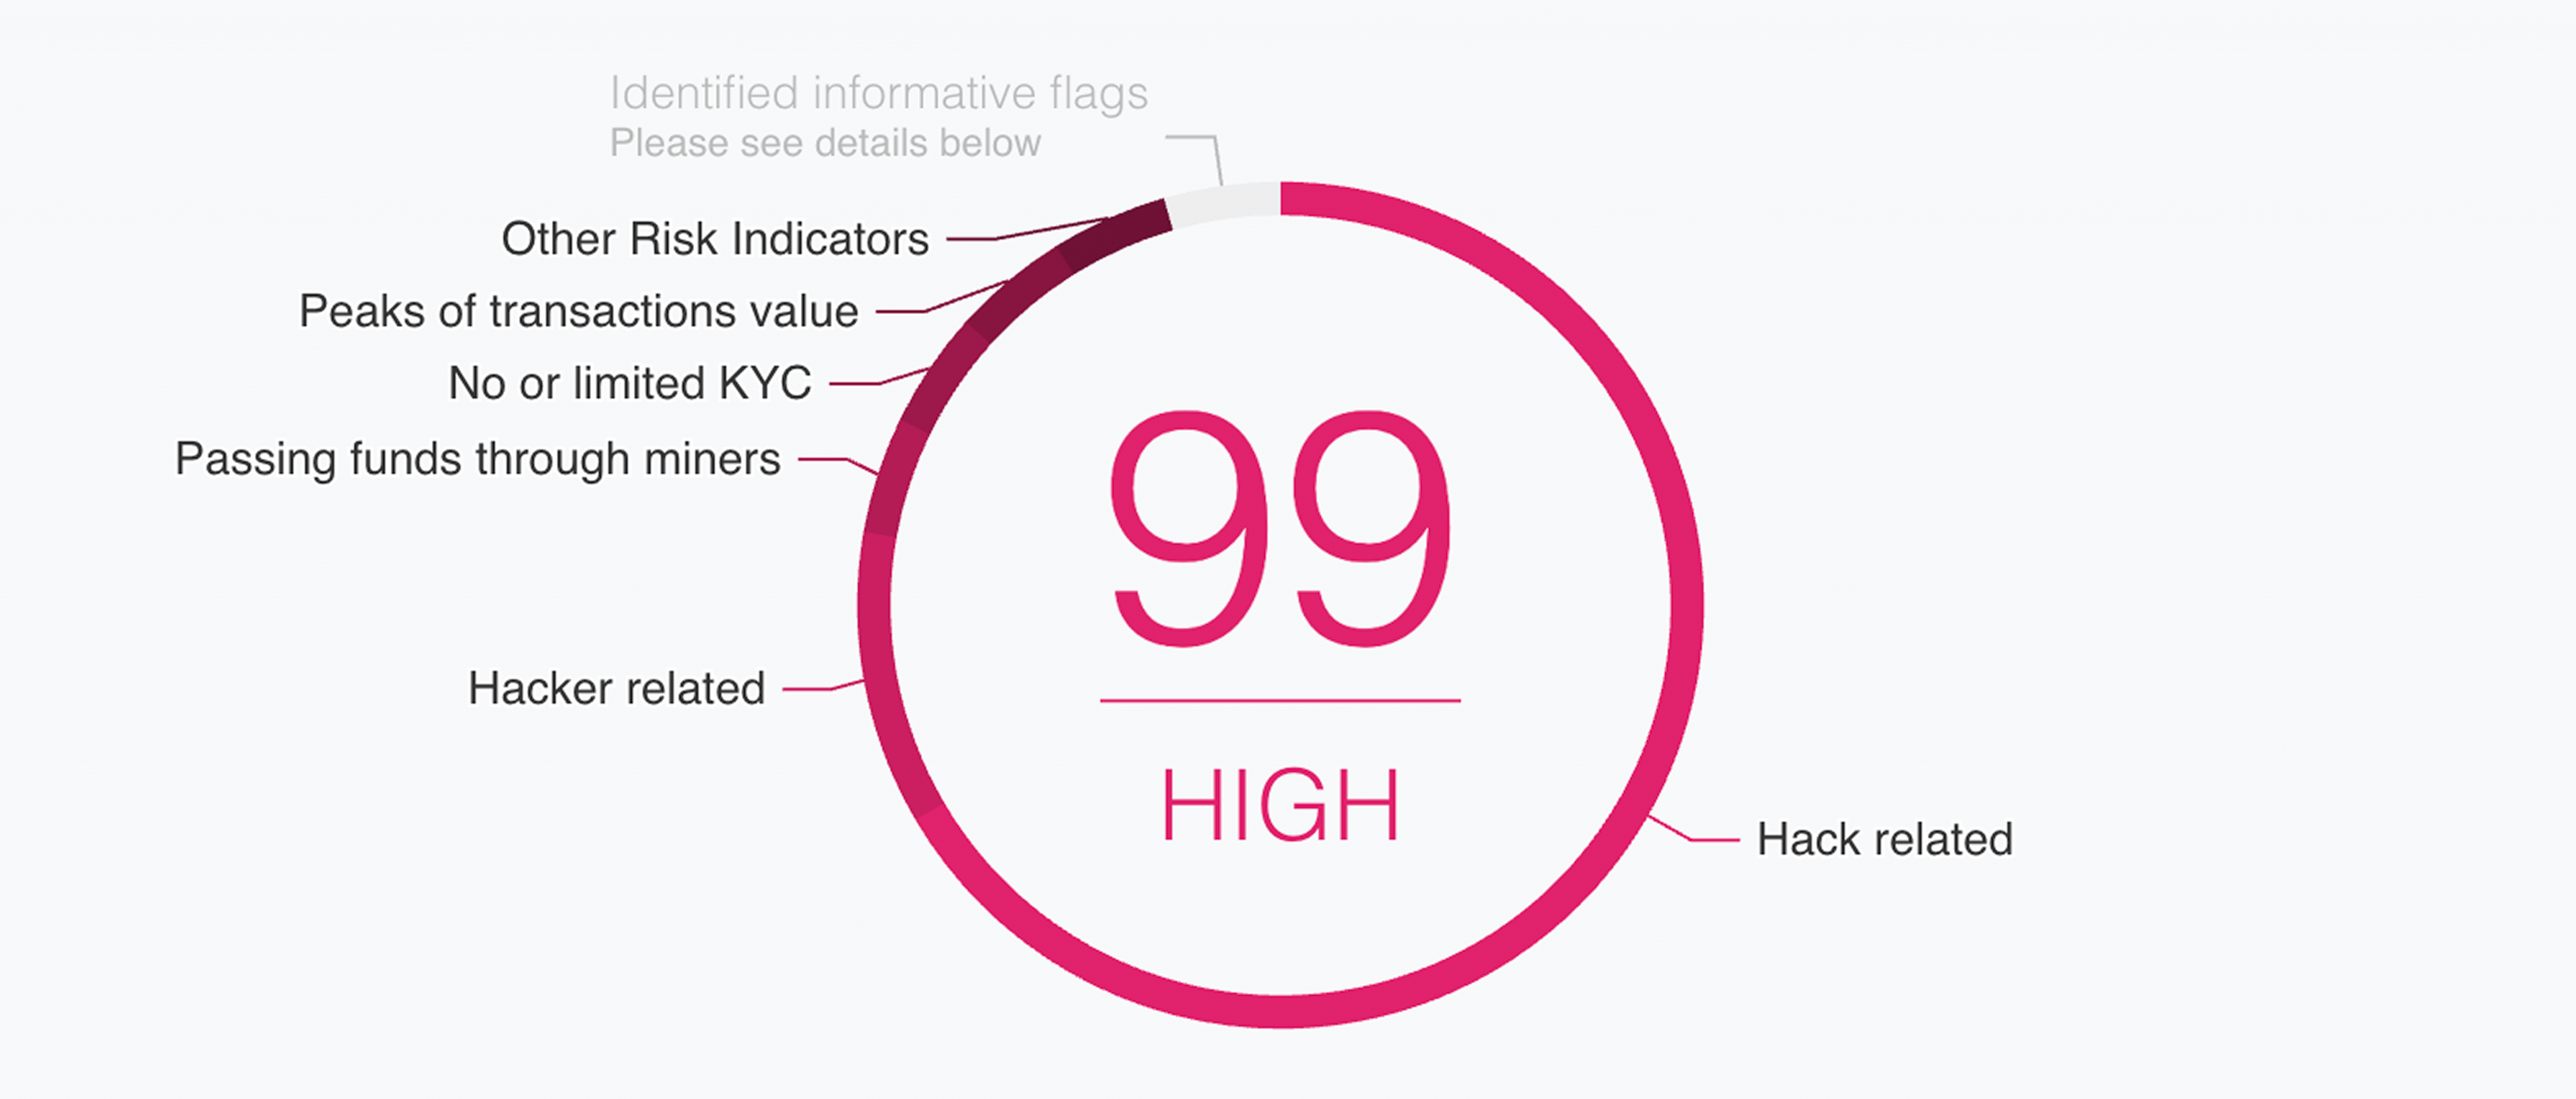
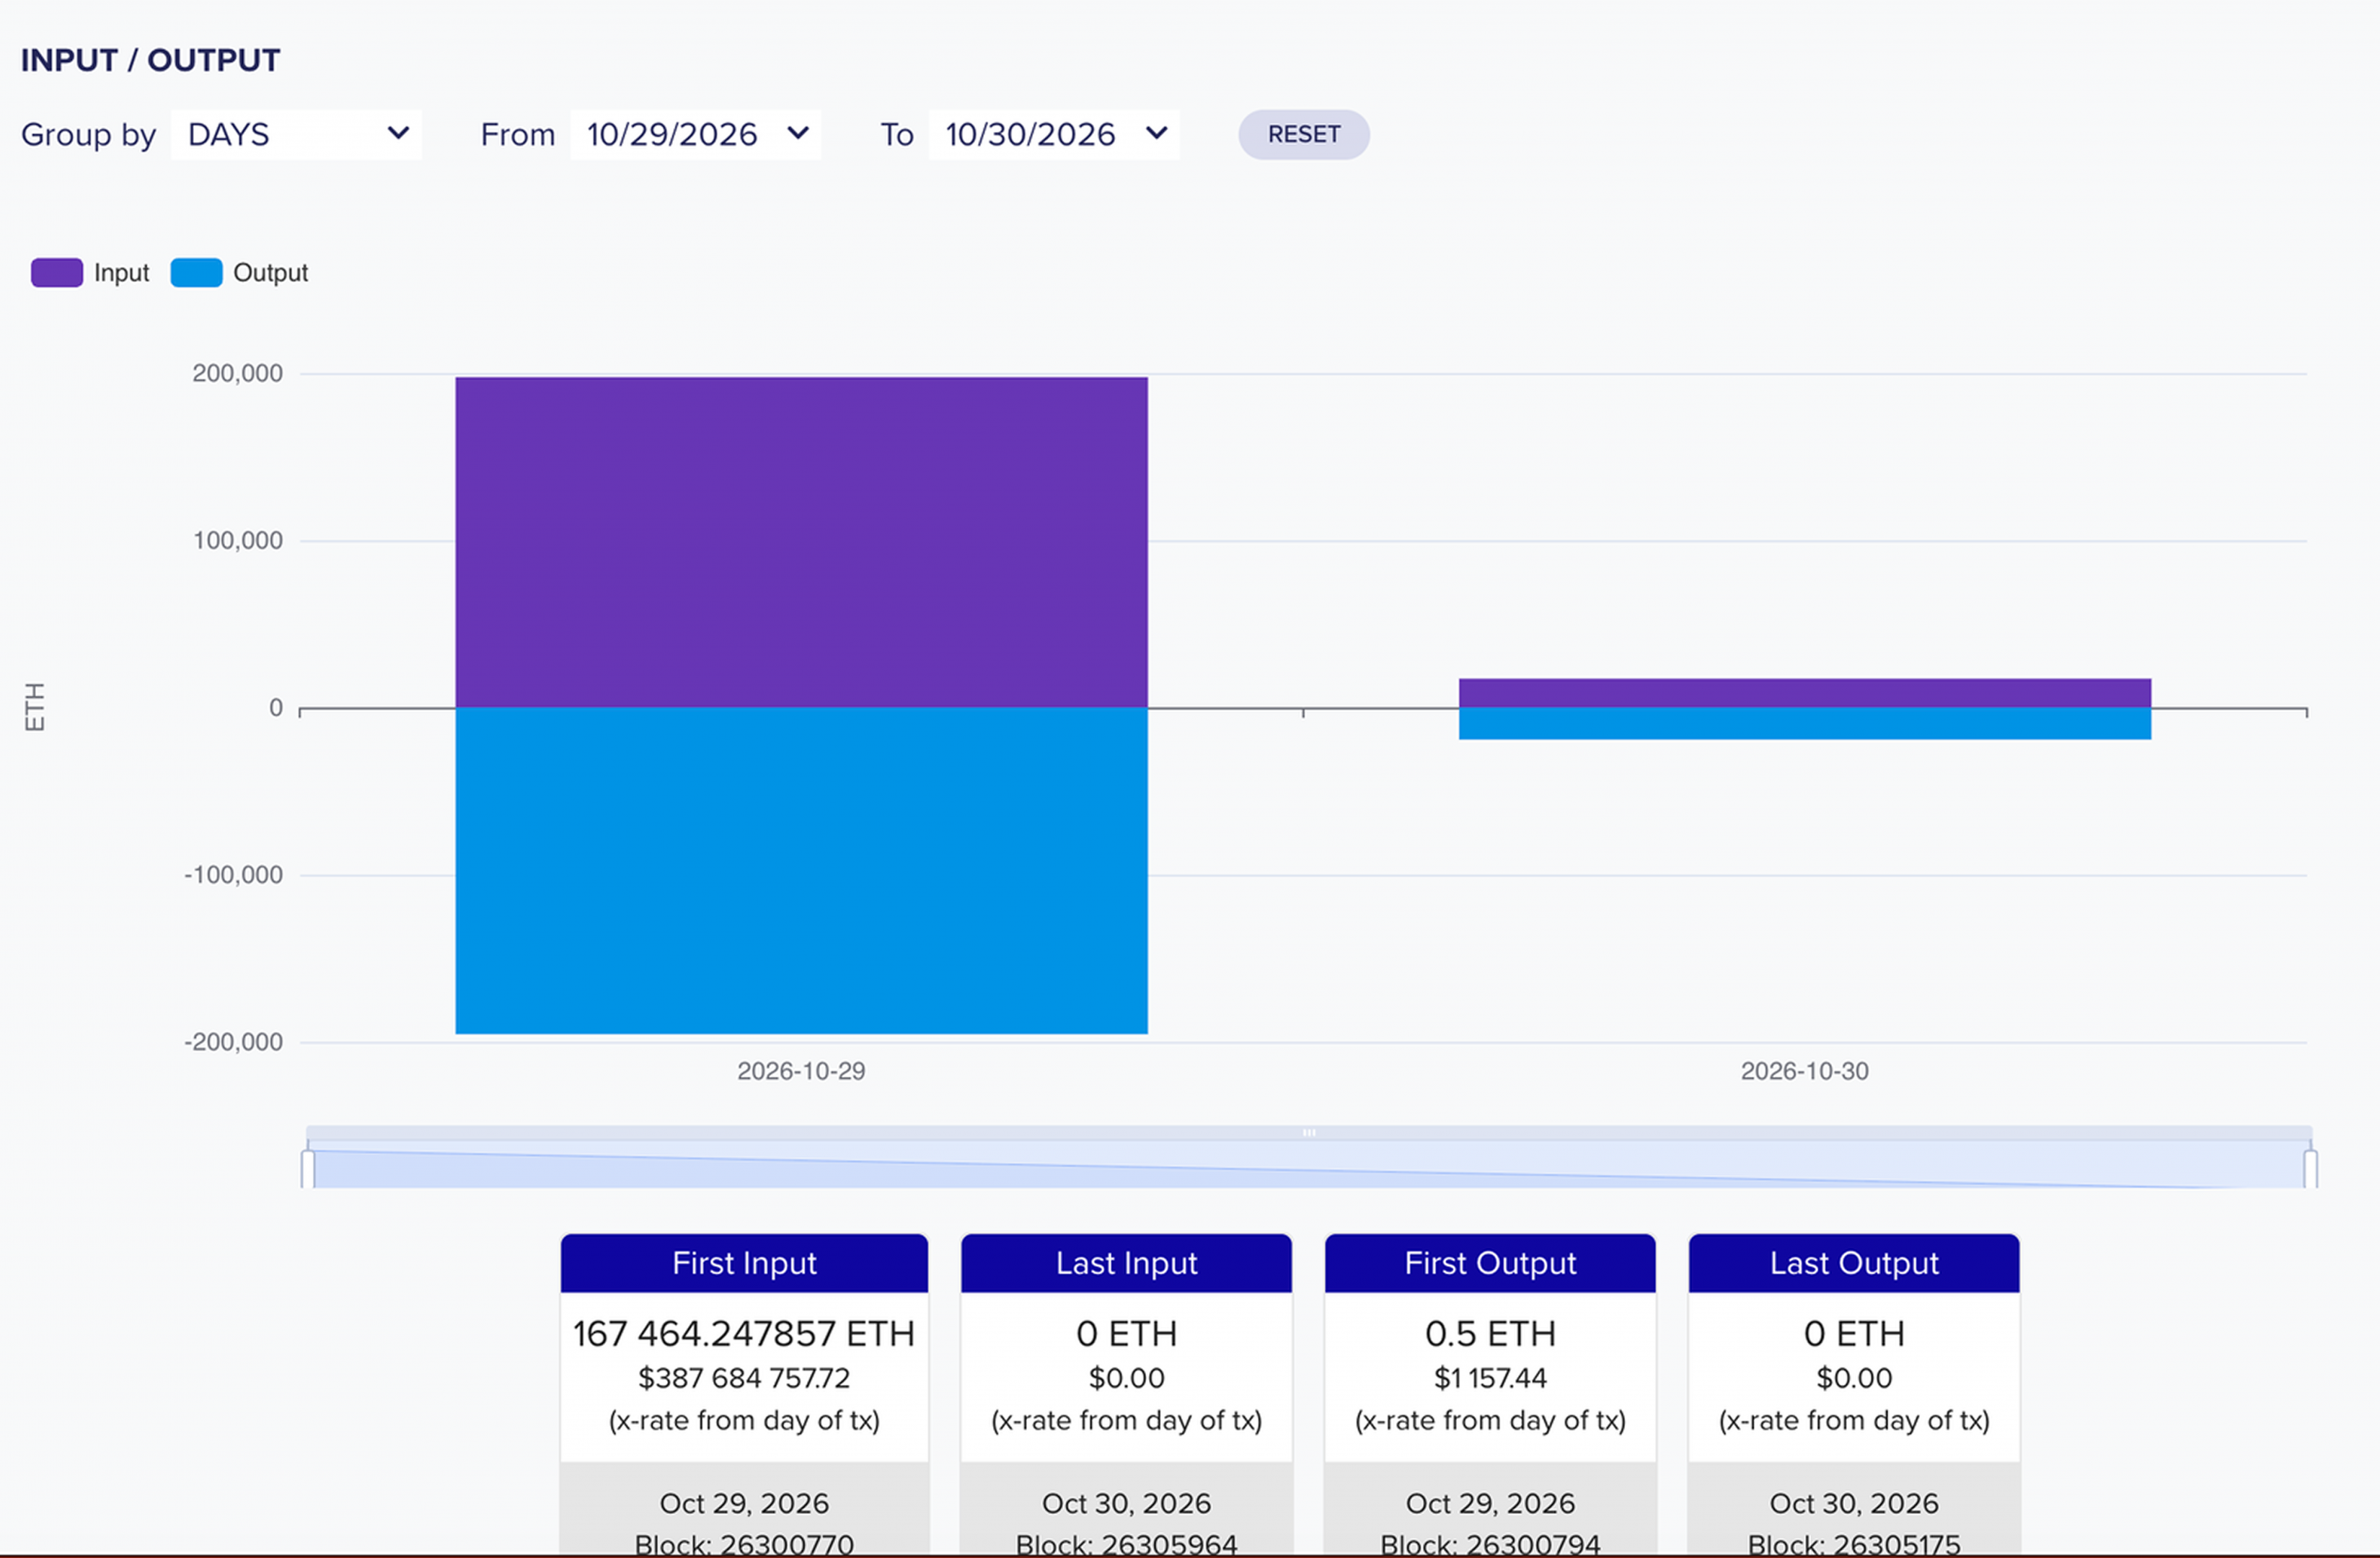
What could move, moved. The wallet’s first incoming transaction was the main sweep: 167,464 ETH, worth about $388 million, at 20:24 UTC on October 29. Five minutes later it sent its first outgoing transfer, a 0.5 ETH test of the route. Over the following days, about 214,700 ETH flowed in and the same amount flowed out across 1,078 transactions. The largest single outflow was 195,460 ETH, worth more than $430 million. The wallet now holds almost no ETH, and its last outgoing transaction was on October 31.
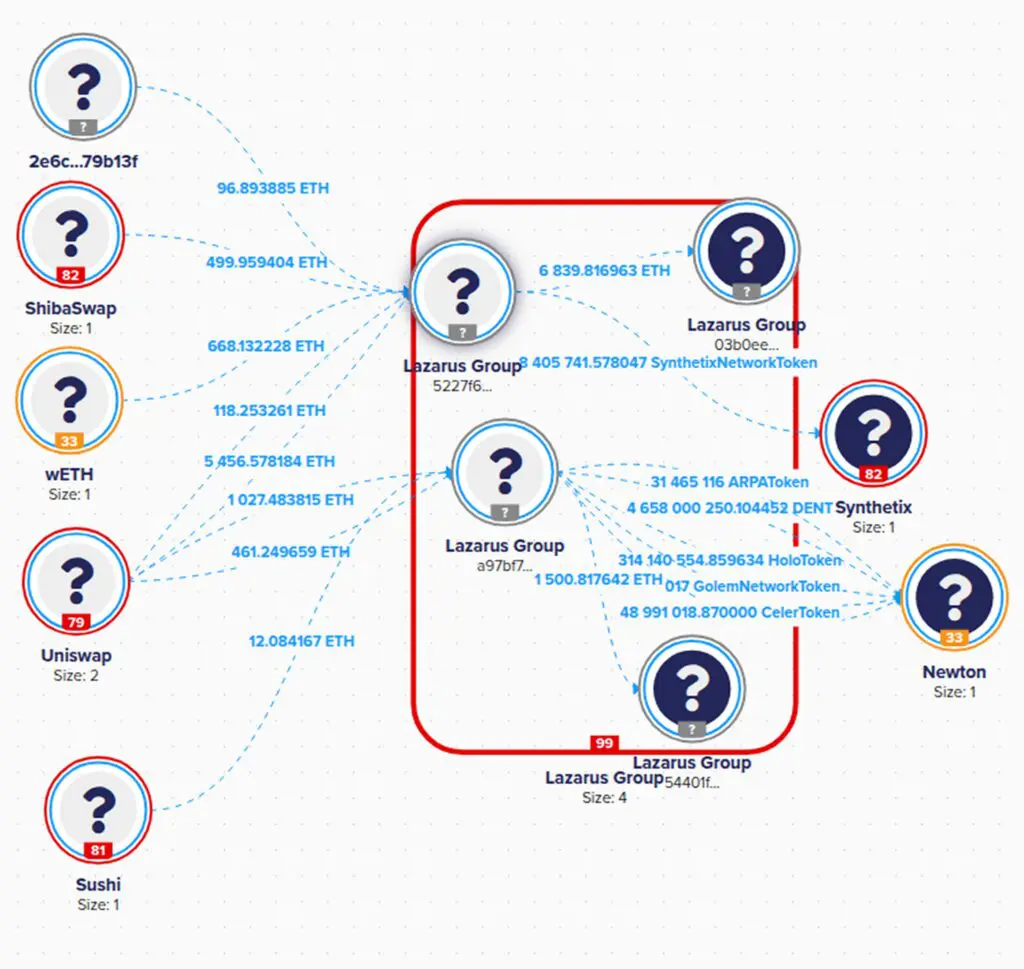
Where it went. Lukka’s exposure analysis shows the largest downstream flows going to two addresses one hop away, both attributed to the same Lazarus Group cluster, carrying roughly $450 million and $200 million in value. It also shows swaps through decentralized exchanges such as Uniswap, and about $60 million reaching the lending protocol Aave within four hops. That matches public reports that an attacker wallet posted 60 million USDT on Aave as collateral to borrow ETH before Aave froze the affected markets.
What could be frozen, stayed. The wallet still holds about $2.06 billion, almost all of it frozen stablecoins: about 1.175 billion USDT and 823 million USDC, plus roughly $58 million in tokenized gold (XAUt and PAXG).
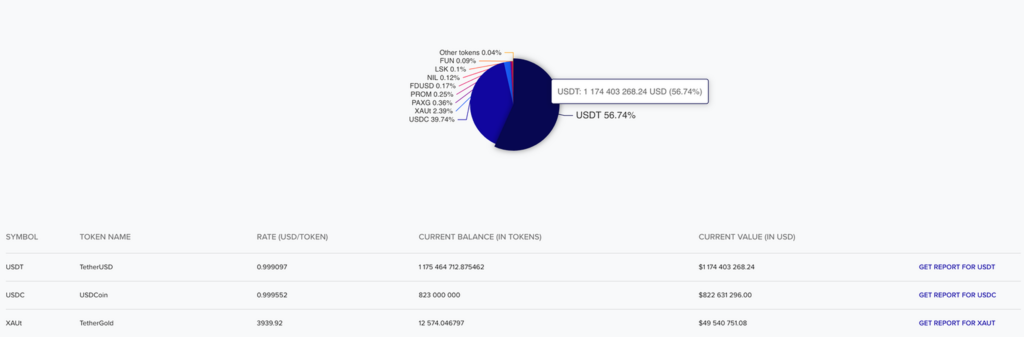
The two halves of this wallet tell the story of the whole incident. Issuers can freeze what they issue, and they acted within 37 minutes. Everything else was gone before anyone could stop it.
One hop downstream: what layering looks like
The second address, 0x15104a9ce0f08a8f0075a0869ae80e795fe0feb7, shows the next stage. Public on-chain reporting has linked it to proceeds of both this theft and the September 2026 exploit of Bitget, which suggests the two incidents share laundering infrastructure. Lukka scores it 99, high risk, flags it as part of a layering scheme tied to hacked funds, and attributes it to the same Lazarus Group cluster as the main wallet.
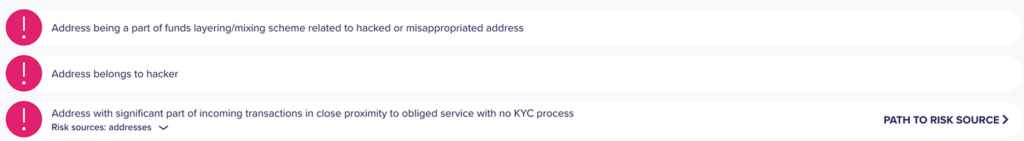
Its activity is a textbook pass-through:
Cross-chain in. Some of its incoming value sits within two hops of THORChain, a cross-chain swap protocol, consistent with funds arriving from another blockchain.
Short-lived. Its first deposit, 71.4 ETH, arrived at 00:30 UTC on October 30. Its last meaningful transfer out was at 08:21 the same morning.
Consolidate, then move. Its first outgoing transfer, 259 ETH, came about 90 minutes after the first deposit, bundling several smaller inflows into one payment.
In equals out. 574.9 ETH came in and 574.9 ETH went out, about $1.3 million each way. It now holds less than $6.
None of these patterns proves wrongdoing on its own. Together, on an address linked to a labeled hack, they are exactly what transaction monitoring should catch before funds reach an off-ramp.
How the money moved

Stablecoins that could be frozen stayed where they were. Ether left the main wallet within hours for other addresses in the same Lazarus Group cluster, and the remaining native assets are now moving toward the exchanges, OTC desks and payment firms where screening can stop them.
Where the money is now
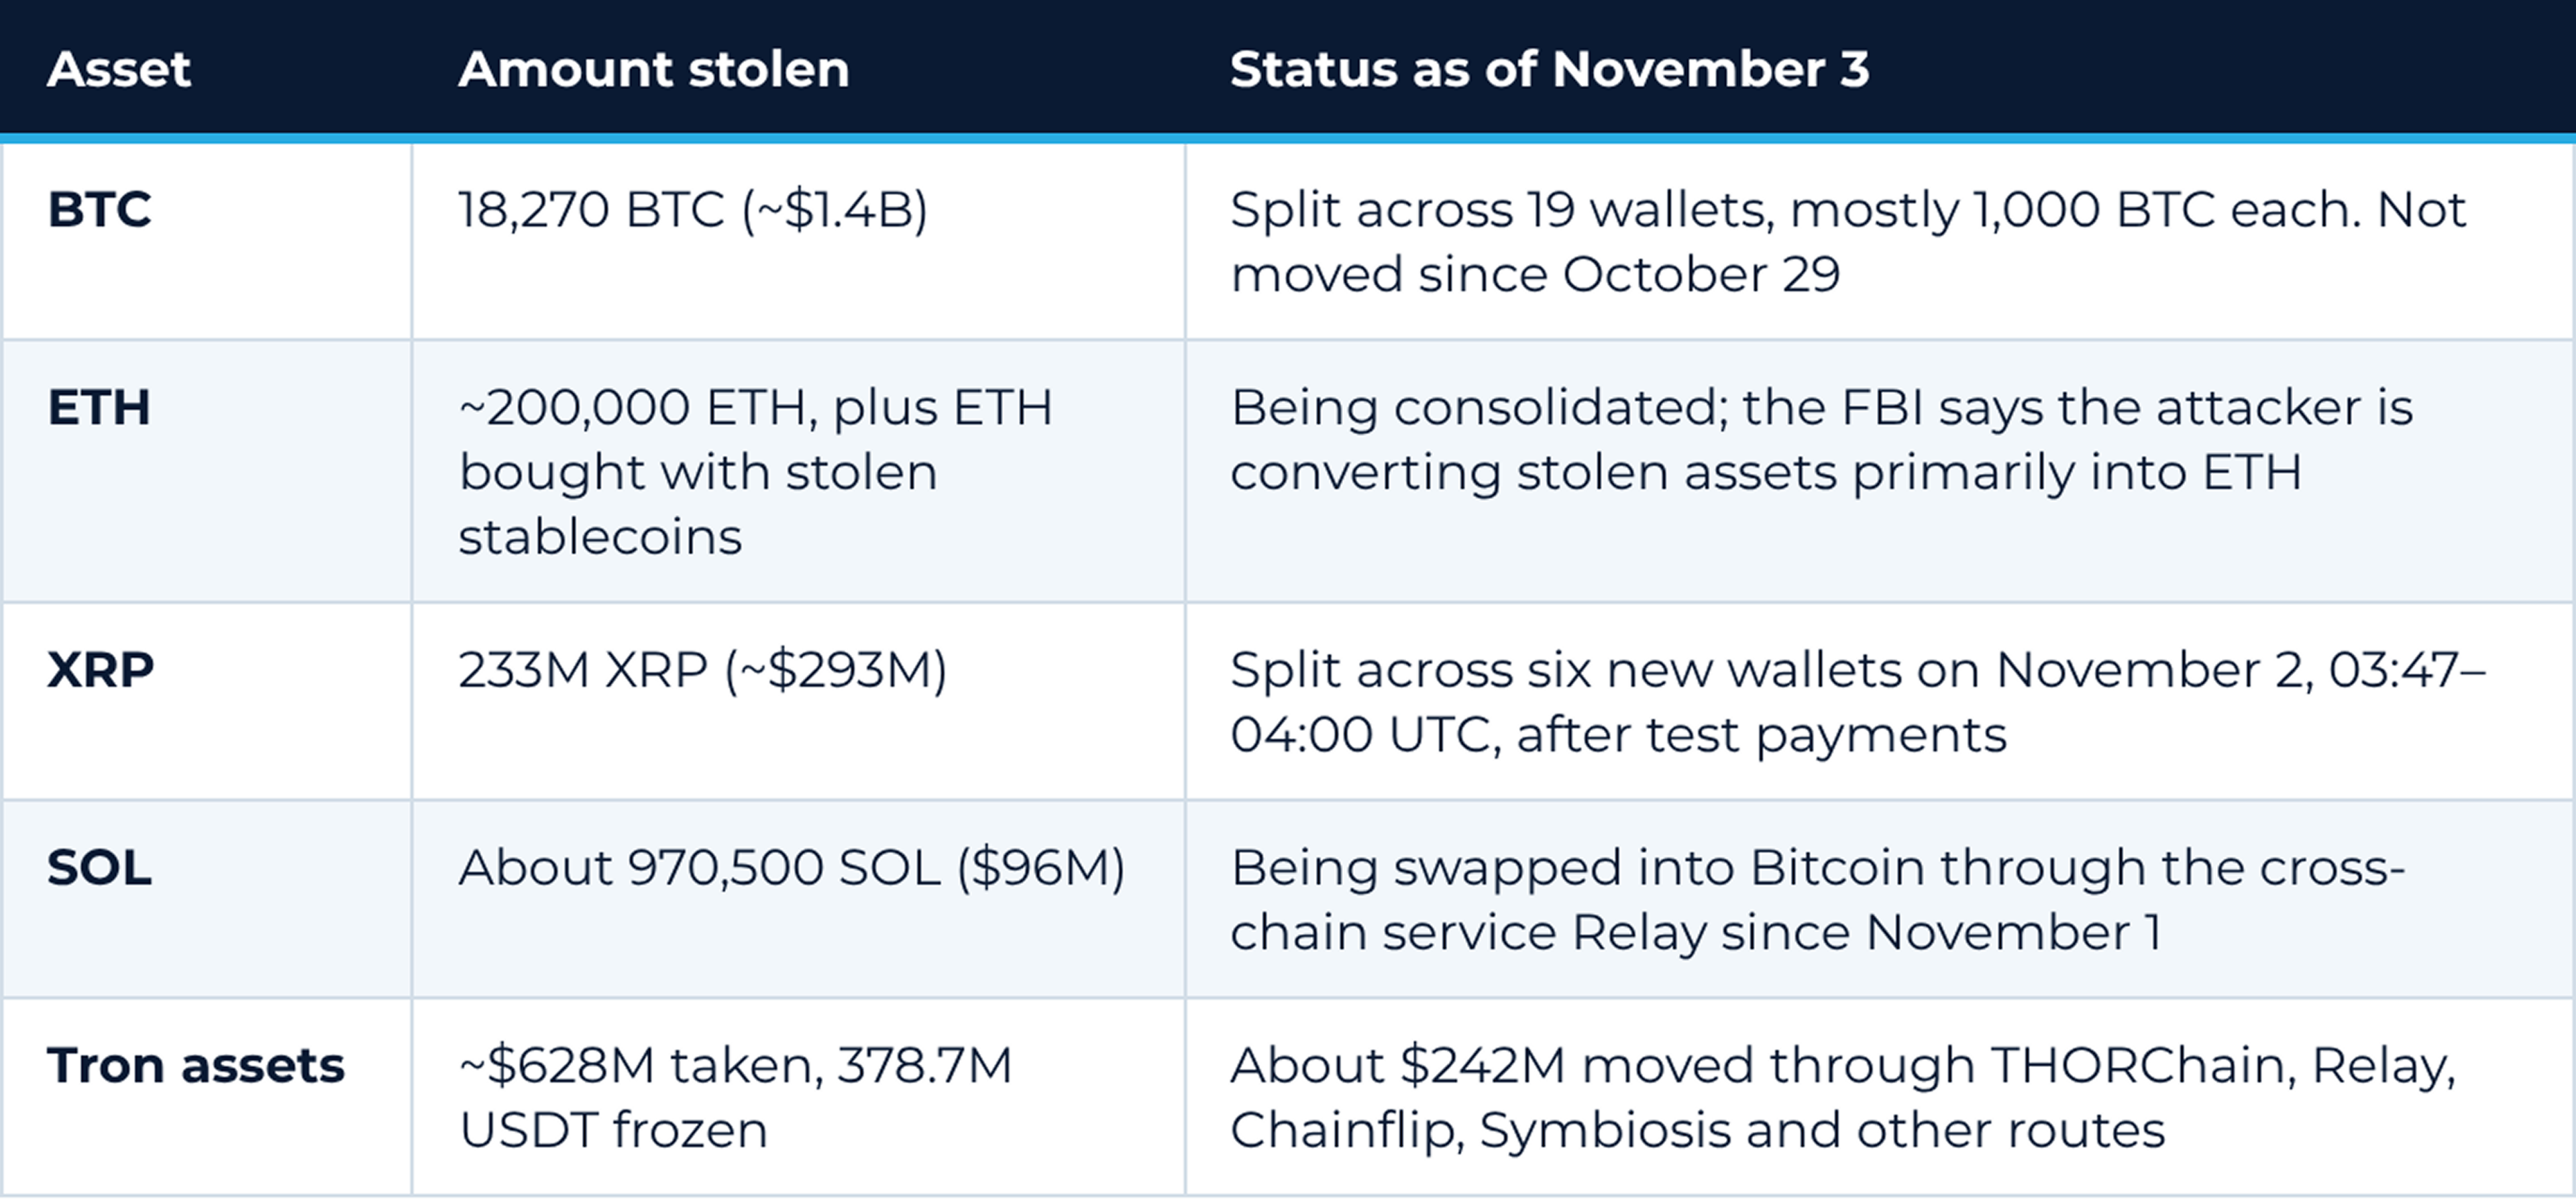
More than $3 billion in assets that cannot be frozen remains under the attacker’s control. Over the weekend, it started to move.
Bitcoin shows how the split works. In Lukka Blockchain Investigator, the 18,270 BTC moves from a Binance hot wallet to a single Lazarus Group address, which divides it into round 1,000 BTC pieces, some routed through intermediate wallets first. Every wallet at the end of the trace is attributed to Lazarus Group and scored 99, high risk.
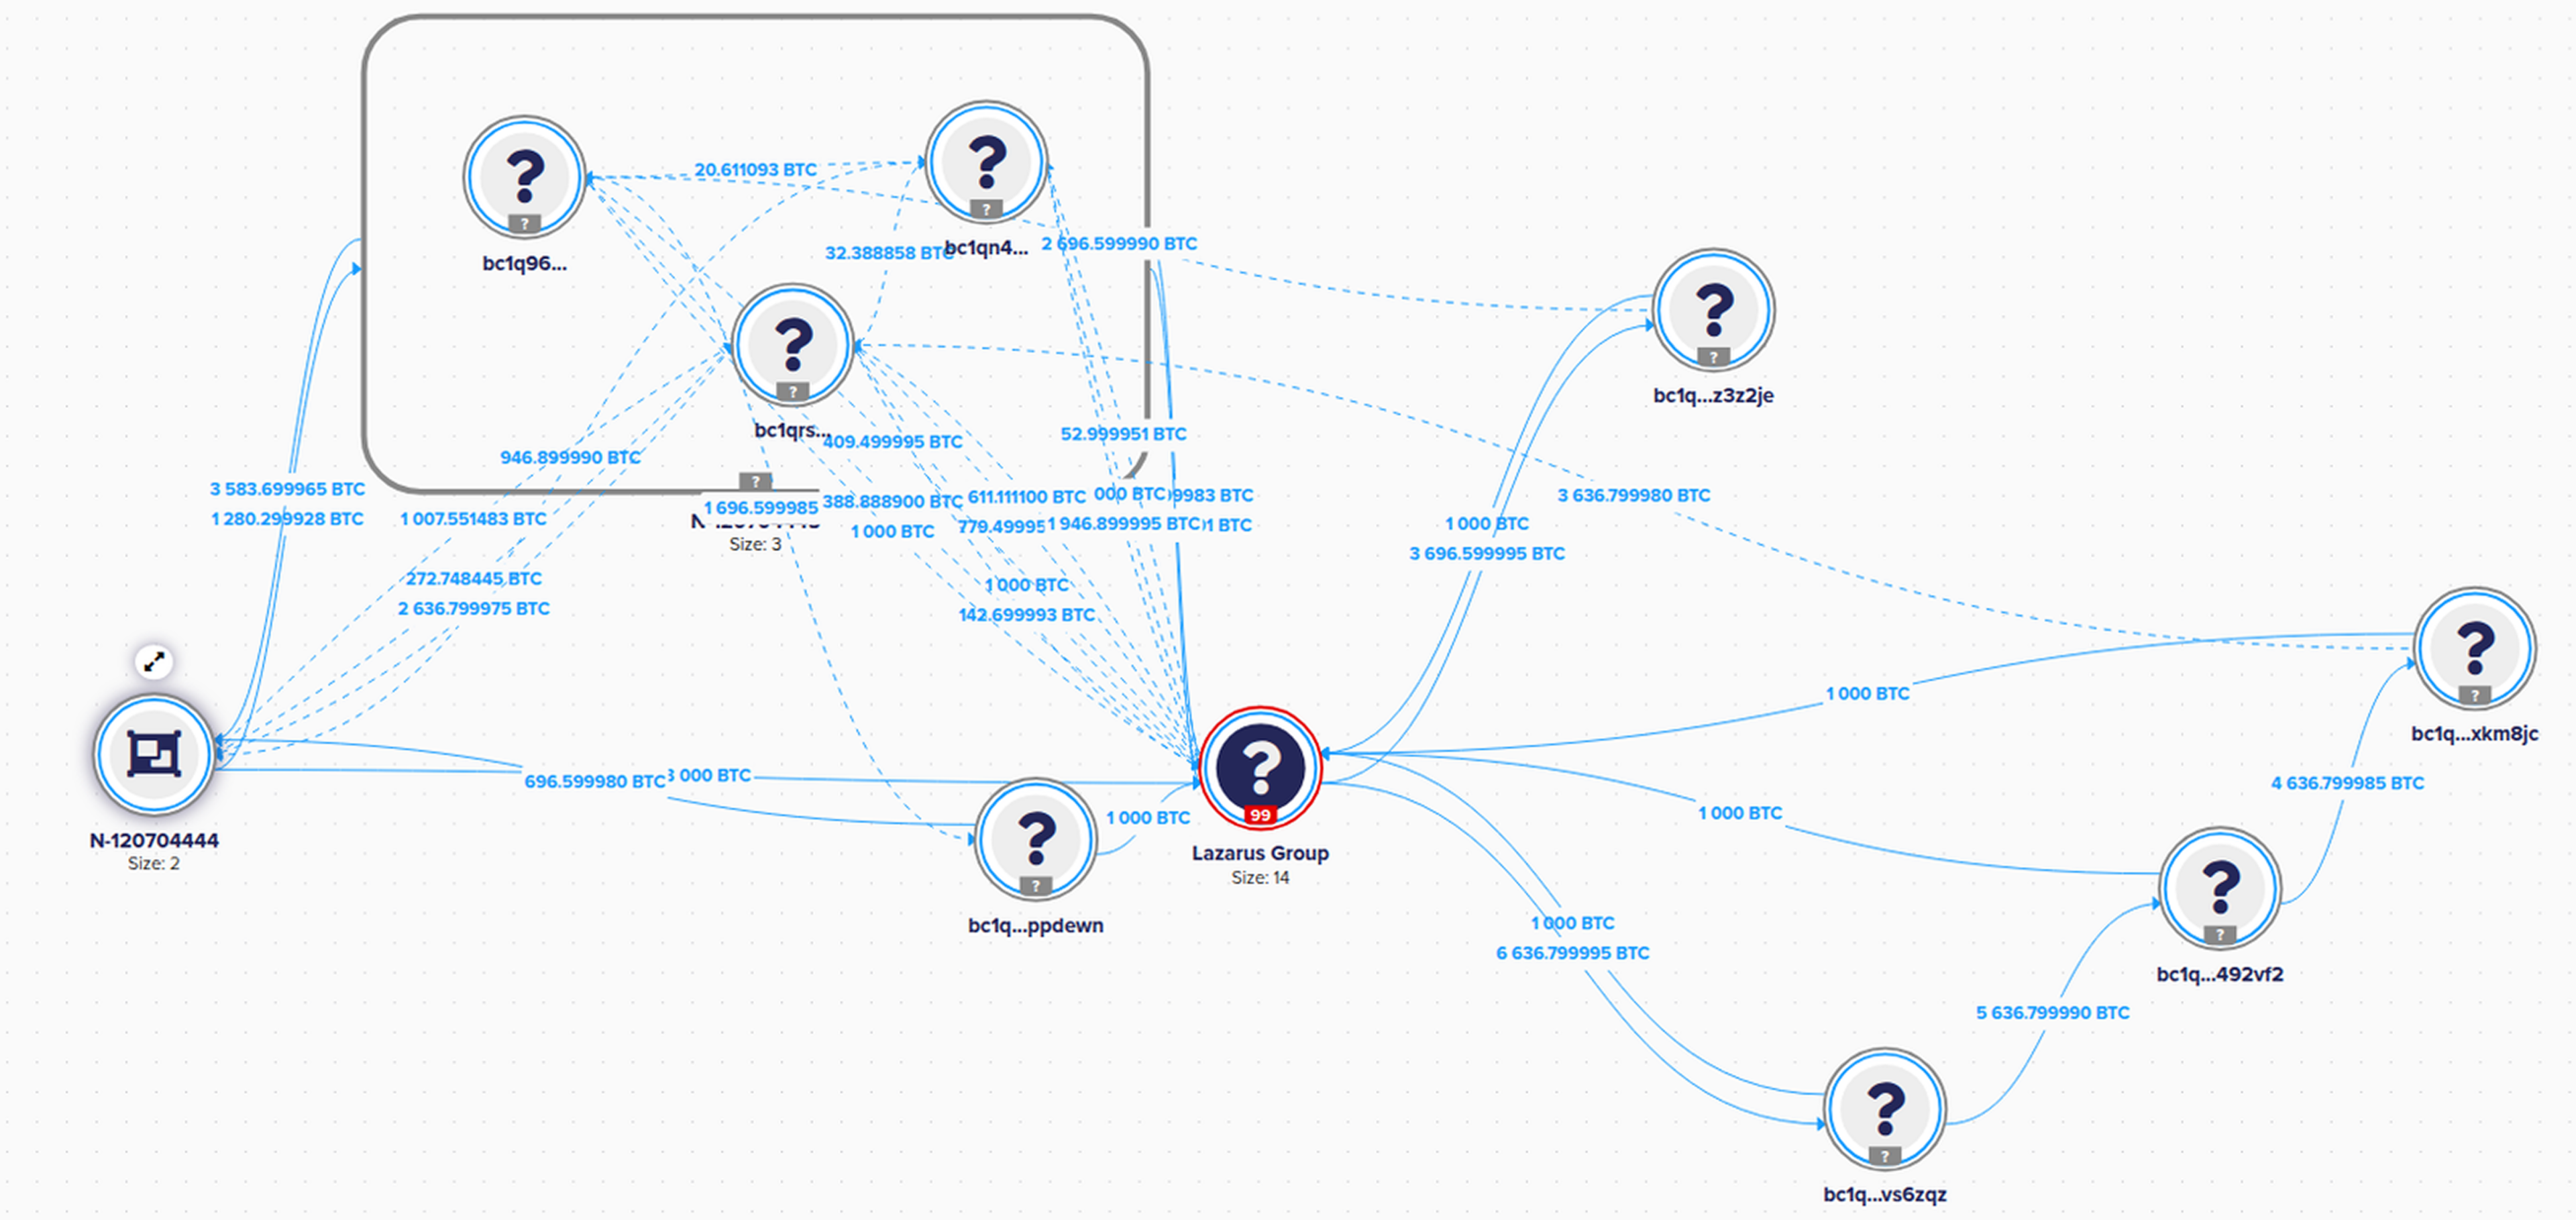
Grouped by owner, the same trace collapses into a single Lazarus Group entity. This is how one attributed address exposes the rest of the network.
Three details matter for anyone running a screening program. First, the laundering is industrial in scale: public on-chain analysis counts about 12,000 wallets and more than 40,000 transactions in under four days. Second, mixing has started: about 28 BTC, converted from stolen Tron and Ethereum assets, has passed through CoinJoin transactions since November 1. Third, an unrelated THORChain outage on November 1 halted swaps on 10 networks and temporarily slowed the laundering, so it could pick up again when service resumes. Small amounts have also been reported arriving at a centralized exchange. Attempts to reach exit points have begun.
Why this goes beyond a hack
It is a sanctions problem, not only a theft. Lazarus Group has been on the U.S. Treasury’s sanctions list since 2019, and the FBI has now tied these funds to North Korea. An institution that processes them is not just handling stolen property; it may be facilitating a sanctioned state. U.S. authorities have long linked North Korea’s crypto thefts to funding its weapons programs.
The scale breaks old assumptions. A single attack took more than four times the previous record, from the world’s largest exchange, in about 20 minutes. Even Binance’s response, covering about $6 billion from its own reserves within three days, is something few institutions could replicate.
Frozen is not recovered. The roughly $3 billion that issuers froze is out of the attacker’s reach, but it has not been returned. Everything that could not be frozen will be laundered through bridges, swap services and, eventually, regulated businesses that may not realize what they are receiving.
The window is now. After large thefts, laundering typically runs for weeks or months. Every hop between the attacker’s wallets and a cash-out point is a chance to identify the funds, but only for institutions screening against current data. With the funds already spread across about 12,000 wallets, no team can watch every hop by hand; it takes monitoring that follows the funds automatically as they move.
How investigators follow funds like these
Public blockchains record every transfer, but a raw transaction history is just strings of characters. Turning it into evidence takes five steps, and each one depends on the quality of the underlying data. This is the workflow Lukka Blockchain Analytics and Lukka Blockchain Investigator are built to support.
1. Attribute. Identify who controls the addresses involved: the victim’s hot wallets, the attacker’s receiving wallets, and the services funds pass through. Lukka has attributed more than 1.2 billion addresses and identifies 50,000+ entities, including exchanges, VASPs and DeFi protocols.
2. Cluster. Group addresses controlled by the same actor, so one labeled wallet exposes the rest of the network. In this case, that turned a single hacker address into a cluster of 10,161 addresses attributed to Lazarus Group.
3. Trace. Follow the funds hop by hop, across chains and through swaps, until they stop or reach an identified service. Lukka Blockchain Investigator tracks funds to their destination, accounts for value lost along the way to fees and dust, and keeps the trace running automatically as new blocks arrive, so the picture updates without anyone re-running it.
4. Score. Apply risk indicators to every address and transaction that touches the funds. Lukka’s model uses 380+ indicators, including sanctions, hacks, mixers and services with no KYC, and shows the reasons behind each score, such as the specific hacker-linked addresses and how many hops away they sit.
5. Monitor and act. Screen deposits and counterparties in real time and put flagged addresses under automated monitoring, so new transactions are picked up as they happen instead of by an analyst watching a screen. Open a case that documents the evidence for internal review, regulators and law enforcement.
The speed of the first two steps decides the outcome of the rest. Issuers froze about $3 billion in this incident because the stolen stablecoins were identified and acted on within the first hour.
Staying vigilant: what compliance teams should do now
1. Screen against the FBI’s published addresses and current attribution data. Addresses tied to this theft are being labeled as funds move. A list that is a day old will miss the next hop.
2. Run a look-back. Re-screen deposits, withdrawals and counterparty flows from October 28 onward, when the attacker’s wallet was first funded.
3. Treat hits as potential sanctions exposure. Route alerts linked to this incident through your sanctions process, not only your fraud or AML queue.
4. Watch for the patterns, not just the addresses. Round-lot Bitcoin deposits of 1,000 or 100 BTC, newly created wallets that pass funds straight through, large ETH or BTC deposits arriving from cross-chain swap services, and XRP from recently created wallets all deserve a second look.
5. Extend due diligence to counterparties. Ask the exchanges, OTC desks, market makers and liquidity providers you deal with how they are screening for these funds. In the first hours, roughly 325 million USDT was sold to market makers and solvers by a wallet that had received it from the hack minutes earlier.
6. Have the case workflow ready. When an alert fires, your team should be able to trace the source of funds, document it, escalate it and support any reporting obligations, with an audit trail a regulator can follow.
7. Check your own signing controls. Review who can request signatures, monitor treasury wallets for unexpected EIP-7702 delegations, and confirm approval paths are separated by chain and wallet tier.
How Lukka helps
The wallet analysis in this post came from the same tools Lukka customers use for screening and investigations every day. Lukka Blockchain Analytics gives compliance and investigations teams what they need for an incident like this one:
Wallet screening and AML risk scoring across 109+ blockchains, drawing on 1.2B+ attributed addresses and 380+ risk indicators covering sanctions, hacks, mixers and other illicit activity, with the evidence behind every score.
Real-time and transaction-level screening for source-of-funds checks on deposits and pre-transaction screening on withdrawals.
Lukka Blockchain Investigator to visualize and trace funds across wallets and chains and follow them to their destination. Tracking and monitoring run automatically: as new transactions come in, Investigator updates the trace and flags new activity, so investigators don’t have to watch addresses manually. Cases are managed from first alert to final report.
VASP Data covering 50K+ VASPs and entities, so counterparty due diligence reflects who you are actually dealing with.
To see how Lukka Blockchain Analytics and Lukka Blockchain Investigator can help your team attribute, trace and investigate illicit funds, from the first alert to a regulator-ready case, request a demo.